Is it Time for a Registration Operations Industry Association? Part II
In Part I of this series of blog posts I described the need for an industry association of operators to discuss the technical tasks, such as the development, deployment, and ongoing systems administration of the Extensible Provisioning Protocol (EPP), performed by registries and registrars to ensure interoperability and share best practices when providing registration services. In this blog post I’ll describe a way to make that happen.
I’ve spoken to a number of registrars who have described the challenges they face in implementing the many different EPP extensions being developed by registry operators. Here’s a concrete example: the Net::DRI Perl implementation of an EPP client includes contact extensions for 24 different registries. A registrar that wishes to manage contacts with those registries needs to implement a contact extension for each one! With the addition of new gTLDs and many new registry operators with new business models the number of extensions can only increase. How would an industry association address these challenges and reduce confusion for everyone? How could an association be structured?
Is it Time for a Registration Operations Industry Association?
Since 2001 there have been occasional conversations on technical mailing lists exploring the concept of creating an independent industry association or consortium of domain registration operators. My recent experiences with the evolution of extensions to the Extensible Provisioning Protocol (EPP) have convinced me to look at these suggestions more closely, and I’m now convinced that this is an idea worth exploring.
“Registration Operations” refers to the technical tasks, such as the development, deployment, and ongoing systems administration of EPP, performed by registries and registrars to provide registration services. While EPP is used to provide domain name registration and management services, registration operations also include the tasks performed by Regional Internet Registries (RIRs) to provide address registration and systems administration services.
Verisign Mitigates 300 Gbps DDoS Attack and Other Q2 2014 DDoS Trends
It has been another busy quarter for the team that works on our DDoS Protection Services here at Verisign. As detailed in the recent release of our Q2 2014 DDoS Trends Report, from April to June of this year, we not only saw a jump in frequency and size of attacks against our customers, we witnessed the largest DDoS attack we’ve ever observed and mitigated – an attack over 300 Gbps against one of our Media and Entertainment customers.
Website Usage Analysis in the New gTLDs
A recent study, by EURid and the Leuven Statistics Research Centre, set out to better understand the most common usage of websites that are linked to domains, and we thought it would be an interesting exercise to extend similar analysis to the new generic top-level domain (gTLD) market. So, we analyzed all second-level domains registered in new gTLDs according to published zone files on June 29, 2014. Verisign utilizes our own proprietary process for classifying websites, which results in similar classifications to those by EURid. The primary difference is that the Verisign classification method is machine-based and is evaluated for each domain independently, while the EURid approach leveraged samples that humans classified.
Internet Grows to 276 Million Domain Names in the First Quarter of 2014
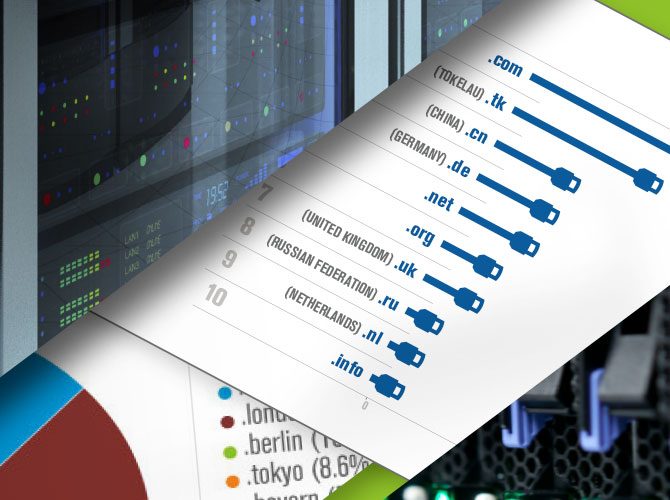
Today, we released the latest issue of the Domain Name Industry Brief, which showed the internet grew by five million domain names in the first quarter of 2014. The total number of domain names across all top-level domains (TLDs) is now 276 million! This is a 1.7 percent increase over the fourth quarter of 2013. [1]
New from Verisign Labs – Measuring Privacy Disclosures in URL Query Strings
Have you ever gone to socially share or email a URL and found that it was much longer than you had expected? Take the following contrived URL as an example:
http://www.example.com/path/submit.php?user=userabc&pageid=012345&utm_referrer=rss&localtime=+0500
In your personal experience, as in our example, you might have realized that the URL was as much about you, the client, as it was about the web resource you were trying to access. Indeed, internet addresses may contain a wealth of information about the identities and activities of the users visiting them. URLs often utilize query strings (i.e., key-value pairs appended to the URL path; in our example, everything after the question mark) as a means to pass session parameters and form data. While sometimes benign and necessary to render the web page, query strings often contain tracking mechanisms, user names, email addresses and other information that users may not wish to publicly reveal. In isolation this is not particularly problematic, but the growth of web 2.0 platforms such as social networks and micro-blogging means such URLs are increasingly being publicly broadcast.
Solving Challenges of Scale in Data and Language
It would not be too much of an exaggeration to say that the early internet operated on the scale of kilobytes, with all spoken languages represented using a single character encoding – ASCII. Today’s global internet, so fundamental to society and the world’s economy, now enables access to orders of magnitude more information, connecting a speakers of a full spectrum of languages.
The research challenges continue to scale along with data volumes and user diversity.
IANA 2.0: Ensuring ICANN Accountability and Transparency for the Future
The National Telecommunications and Information Administration’s (NTIA) March 14, 2014, announcement proposing the transition of its legacy Internet Assigned Numbers Authority (IANA) stewardship role has presented the Internet Corporation for Assigned Names and Numbers (ICANN) multi-stakeholder community equal amounts of opportunity and responsibility. We have been handed a singular opportunity to define the terms of any stewardship transition and the fundamental responsibility to get it right.
Getting it right means ensuring, through a bottom-up, multi-stakeholder process, the reform of ICANN’s accountability structures to protect the community and the multi-stakeholder model prior to NTIA’s disengagement from its oversight and stewardship role. It also means acting quickly and efficiently so our window of opportunity is not missed.
The Evolving Threat of Amplification DDoS Attacks
If there is one trend in the cybersecurity world over the last 12 to 18 months that cannot be ignored, it is the increasing prevalence and destructive power of amplification-based distributed denial of service (DDoS) attacks.
An amplification attack is a two-part DDoS attack that generally uses the User Datagram Protocol (UDP). An attacker first sends a large number of small requests to unsuspecting third-party servers on the internet. The attacker crafts these requests to result in large responses, but they are otherwise normal except that their source addresses are rewritten (spoofed) so they appear to have come from the victim instead of the attacker. When all the third-party servers send their large responses to the victim, the resulting amount of traffic is much more than the attacker could have generated alone. These attacks often overwhelm the resources of the victim, as attacks in the hundreds of gigabits per second (Gbps) are possible using this method.
Verisign Named to the OTA’s 2014 Online Trust Honor Roll
We are pleased to announce that Verisign has made the 2014 Online Trust Honor Roll for demonstrating exceptional data protection, privacy and security in an effort to better protect our customers and brand from the increased threats of cybercriminals.